Agents can help write code, but the commands they run should not receive the keys to the rest of the system. Lagom separates the place where code runs from the connector that can publish a reviewed change.
A boundary around commands
An agent works in its own container, an isolated place to run commands, with a clone of the public repository. Infrastructure credentials do not enter that container. The runner’s connector, not the container, may hold a GitHub token scoped to this one repository, under ADR-0035.
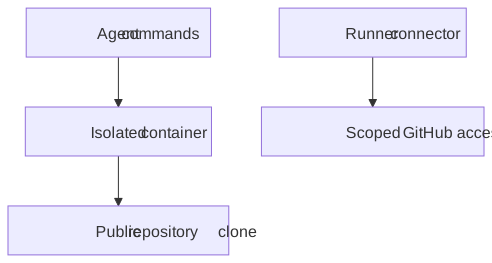
What the boundary does and does not do
The container limits access to credentials; it does not make generated code trustworthy. Changes still need review, and the token’s permissions define what it can change. Isolation has a cost: agents need a deliberate way to share work.